What Emphere Builds
Emphere (Emphere, Inc.) builds an autonomous AI-agent engine that patches open-source Common Vulnerabilities and Exposures (CVEs) directly inside container images and Dockerfiles. On its official website, the company positions the system around taking a team's existing Dockerfile as the sole input—without requiring a registry, scanner, or CI/CD pipeline migration—and returning a rebuilt, clean image across open-source distributions including Ubuntu, Debian, and Alpine.
Under the hood, Emphere decomposes each container image into base operating system layers, runtimes, libraries, and application code at the symbol level so it can trace which vulnerabilities are actually reachable and what a change affects. When an official upstream fix exists, Emphere applies it at the source and rebuilds; for won't-fix findings, zero-day issues, or end-of-life packages without an upstream patch, Emphere's agents write, backport, or bridge a custom patch and continue maintaining it until an official fix ships. As GeekWire reported on June 4, 2026, every rebuilt package passes automated exploit and compatibility checks before release.
- Existing Dockerfile workflow: Ingests a team's current Dockerfile and monitors it as new CVEs appear, keeping existing base images, registries, scanners, and CI/CD pipelines intact.
- Dual validation gates: Runs every patched image through a security gate (rerunning a working exploit against the rebuilt image) and a compatibility gate (functional, integration, and runtime tests), holding the build if either fails.
- Independent audit evidence: Returns Cosign-signed images verifiable against Emphere's public key without an Emphere login, bundled with SLSA provenance, CycloneDX and SPDX SBOMs with embedded reachability, and before-and-after exploit and scan verdicts.
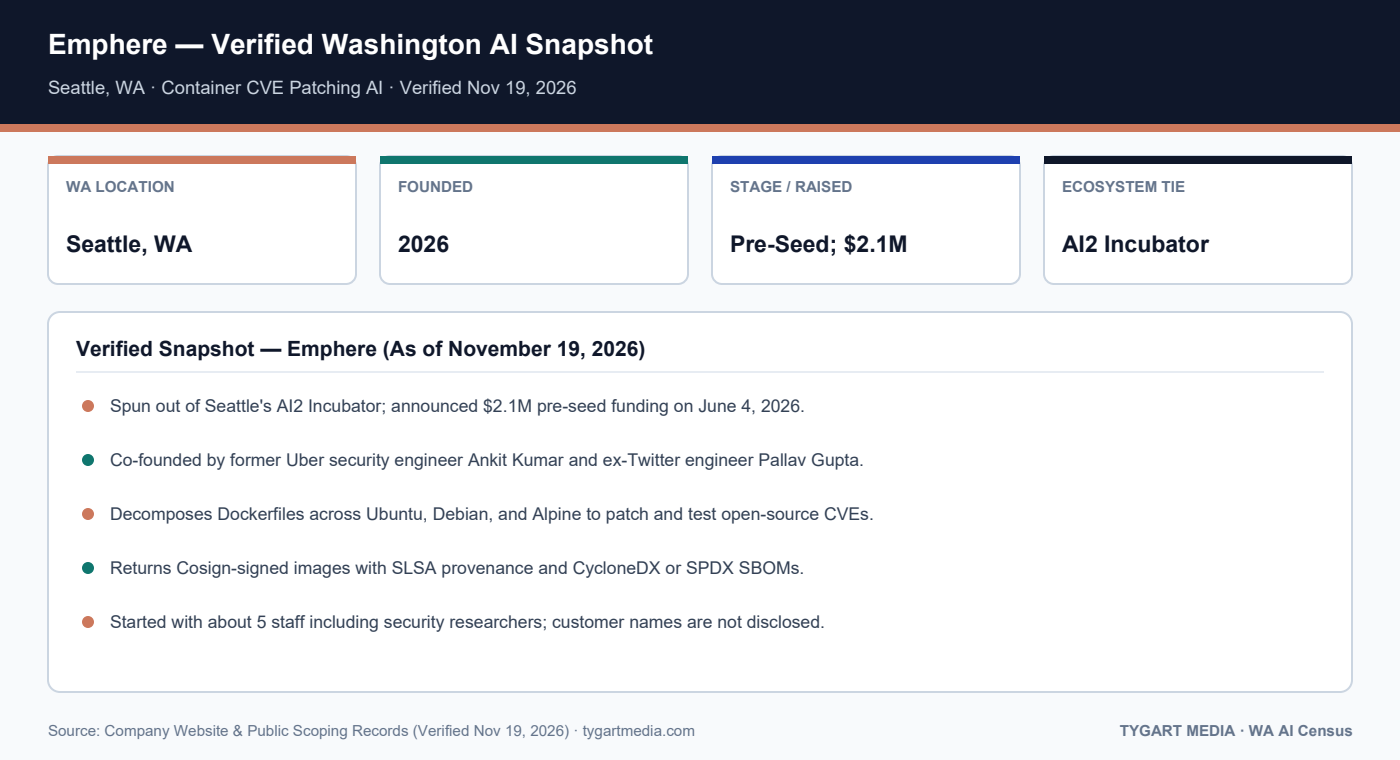
| Field | Verified Record (As of Nov 19, 2026) |
|---|---|
| Company | Emphere (Emphere, Inc.) |
| Official Website | https://emphere.com/ |
| Washington HQ | Seattle, WA |
| Other WA Footprint | Spun out of AI2 Incubator / AI House (Seattle, WA) |
| Founded | 2026 (AI2 Incubator spinout announced June 4, 2026) |
| Founders / Leadership | Ankit Kumar (Co-Founder & CEO), Pallav Gupta (Co-Founder & CTO) |
| Stage | Pre-Seed |
| Announced Funding | $2.1M Pre-Seed (June 2026; AI2 Incubator, Outsiders Fund) |
| Team Size | 5 (as of June 2026 GeekWire report) |
| Primary Ecosystem Ties | AI2 Incubator / AI House (Seattle spinout and investor); GeekWire coverage (June 2026) |
Washington Footprint and Leadership
Emphere is headquartered in Seattle, Washington, and spun out of Seattle's AI2 Incubator. The company appears as an active, unacquired portfolio company in the AI House Incubator directory, where it is described as securing every layer of a team's Dockerfile. Emphere's official web presence operates at emphere.com alongside its About page and LinkedIn company profile.
The startup was co-founded by Ankit Kumar (Co-Founder & CEO), who spent six years working in security at Uber, and Pallav Gupta (Co-Founder & CTO), a former software engineer at CarGurus and Twitter. The two co-founders met as college roommates at Northeastern University. According to GeekWire's June 4, 2026 report, Emphere started with a team of about five people, pairing the two co-founders with security researchers who test and confirm patches.
Products, Users, and Public Traction
Emphere targets product security and platform engineering teams at software, infrastructure, data, security, and developer-tool companies that ship containerized products to enterprise customers and regulated buyers such as banks. On emphere.com, the onboarding flow centers on a contact-led request form allowing prospective teams to upload a Dockerfile (up to 10MB) for review rather than open self-serve signup, and the site does not publish self-serve pricing tiers.
Named customers, deployment counts, and revenue figures are not publicly disclosed in Emphere's site materials or GeekWire reporting. On its homepage, Emphere states operational targets and benchmarks of zero CVEs per release, critical and high CVEs targeted within 24 hours of disclosure, approximately 30% of engineering hours saved per week, and 48 hours to a first clean image; those metrics are company-reported rather than independently audited.
Funding, Stage, and Place in Washington's AI Landscape
Emphere is at the pre-seed stage. On June 4, 2026, GeekWire reported that the startup raised $2.1M in pre-seed funding backed by AI2 Incubator and Outsiders Fund. No subsequent venture round or acquisition has been announced through November 2026.
Within Washington's AI and security ecosystem, Emphere focuses on automated container supply-chain patching rather than alert generation alone. Pairing AI patch synthesis with verifiable Cosign signatures, SLSA provenance, and exploit reruns positions the startup alongside Seattle peers addressing adjacent layers of AI-era software trust, cloud access governance, and automated code verification.
Related Washington AI Profiles & Tygart Media Context
- Certiv — Seattle AI Profile
- StratoCloud — Seattle AI Profile
- TestSprite — Seattle AI Profile
- Why AI Compute Needs a Warranty, Not Another Watermark
Verified Primary Sources
- Emphere Official Website
- Emphere About Page
- Emphere Blog
- Emphere LinkedIn
- GeekWire — Emphere $2.1M Pre-Seed Coverage (June 4, 2026)
- AI House / AI2 Incubator Companies
Get The Signal
What we actually ran, what it measured, and what it means for a restoration shop — every week, including the flops.
Leave a Reply